Pre-Launch Review

Config, headers, and TLS checks Radiantze completes before go-live.

Radiantze Pre-Launch Assurance

Radiantze pre-launch reviews focus on cloud and Firebase rules, HTTP security headers, and TLS, focusing on the settings that most often create real exposure.

Findings include severity and fix guidance so engineering remediates before users or client data rely on the site.

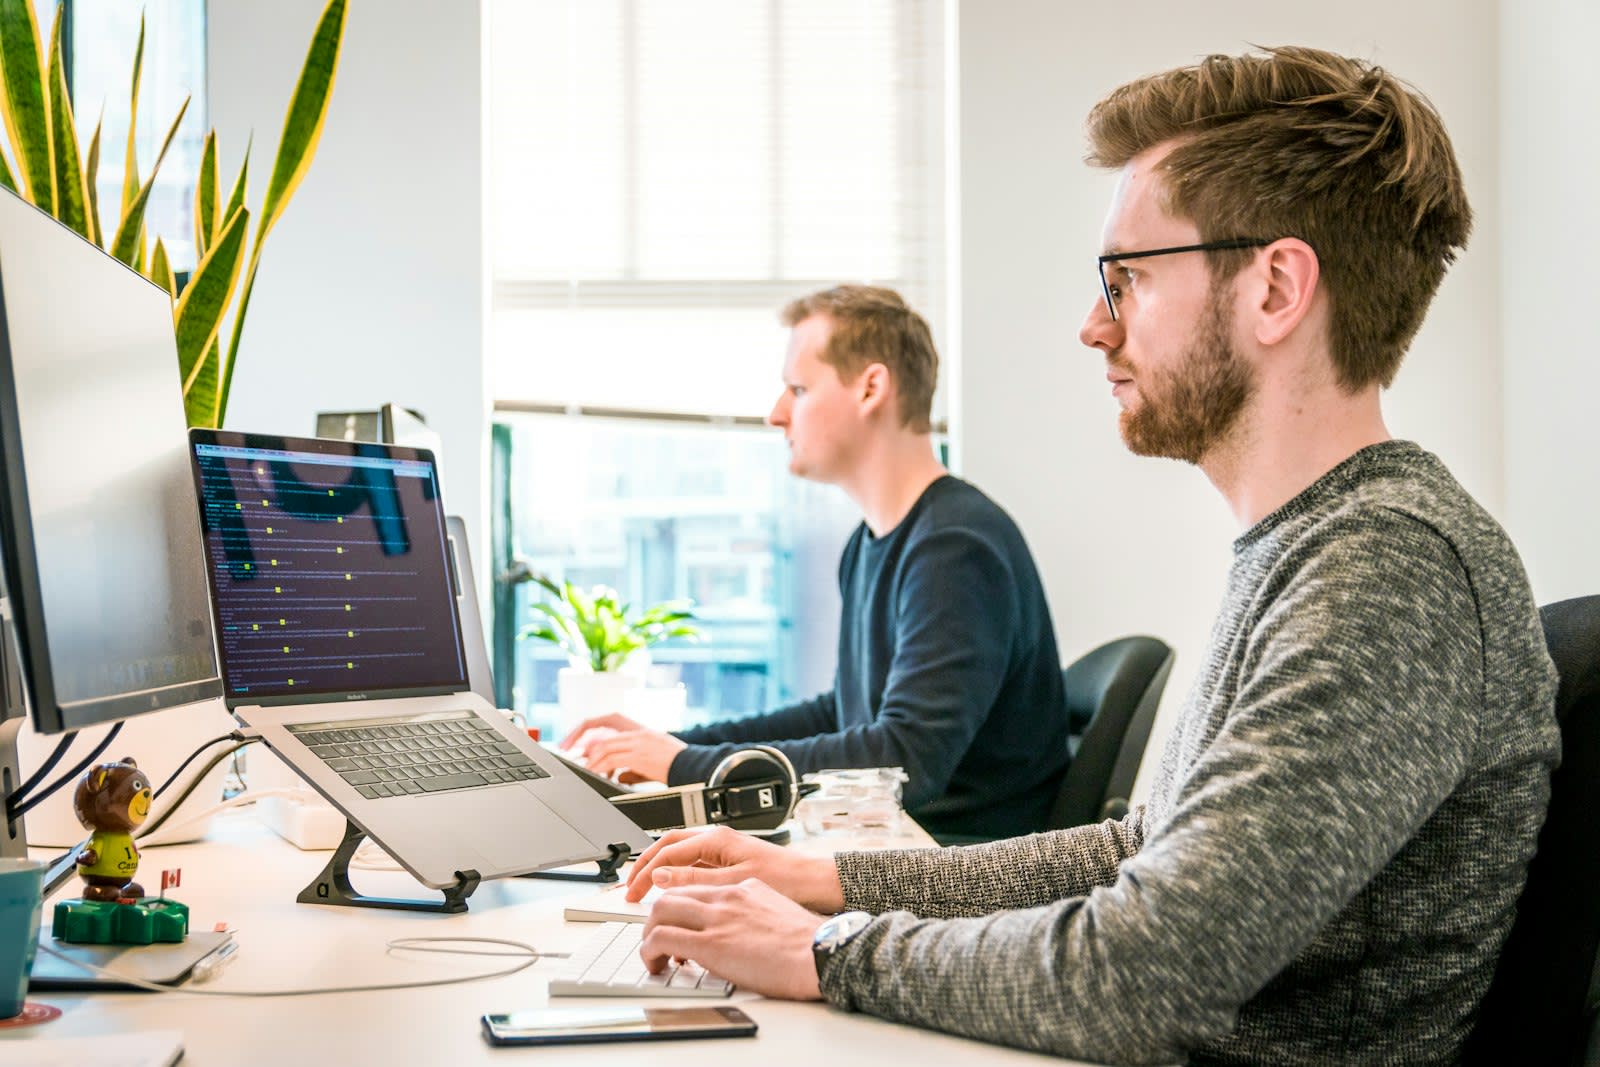
Engineer reviewing application code on a dual-monitor workstation before launch

Partnership

Radiantze Launch Checks

A focused review of the controls that protect data and build buyer trust.

  • Firebase and cloud config audit covering Firestore, Storage, Auth, and Functions permissions.
  • Deny-by-default data rules with Auth and ownership checks.
  • HTTP security headers including CSP, HSTS, X-Frame-Options, and Referrer-Policy.
  • TLS and certificate configuration check for production endpoints.

Radiantze delivery examples

Firebase Rules Audit

Collections and buckets start closed. Access requires proven identity and ownership.

Functions Privilege Review

Service accounts checked for excess permissions. Admin writes stay server-side.

HTTP Header Baseline

CSP, HSTS, framing controls, and referrer policy as practical production defaults.